If you haven’t formally rolled out AI tools at your business, it might feel like this topic doesn’t apply to you yet. It does. Your team is very likely already using AI in some form, whether or not anyone signed off on it.
That’s not a scare tactic. It’s just where things stand heading into the back half of 2026. AI tools have moved from novelty to daily habit faster than almost any technology before them. Most businesses haven’t caught up with a plan for how they should be used. This article walks through a practical AI readiness checklist, five things worth checking before you head into Q4 and start mapping out your 2027 technology plan.
Key Takeaways
- Regular AI use on corporate devices jumped from 15% to 45% in a single year, according to Verizon’s 2026 Data Breach Investigations Report.
- More than half of organizations have no formal policy governing employee AI use, according to KPMG, despite AI already being part of daily work for most teams.
- A 5-point AI readiness checklist, covering tool visibility, data-sharing policy, employee guidelines, sensitive data rules, and shadow AI monitoring, covers the most common gaps.
- Closing these gaps is easier with an experienced IT partner involved, since AI governance works best as an ongoing process rather than a one-time fix.
Why Does AI Governance Matter Right Now?
AI adoption inside businesses didn’t happen through a formal rollout. It happened the way most workplace technology shifts happen now, quietly, tool by tool, employee by employee. An employee drafts an email with ChatGPT. A manager summarizes a meeting with an AI notetaker. Someone else uses an AI tool to speed up a spreadsheet task. None of it feels risky in the moment, and most of the time, it isn’t.
The scale of this shift is easy to underestimate. McKinsey’s November 2025 State of AI survey found that 88% of organizations now regularly use AI in at least one business function, up from 78% just a year earlier. Adoption is moving faster than most internal policies can keep up with.
The risk shows up in the gaps. Not knowing what’s being used or what data is going into it. Not having any policy that tells employees where the lines are. It’s the same pattern we’ve seen with plenty of other technology shifts, but AI moves faster and touches more sensitive data than most.
Building AI governance into your regular planning cycle now is easier than trying to catch up later.
The 5-Point AI Readiness Checklist
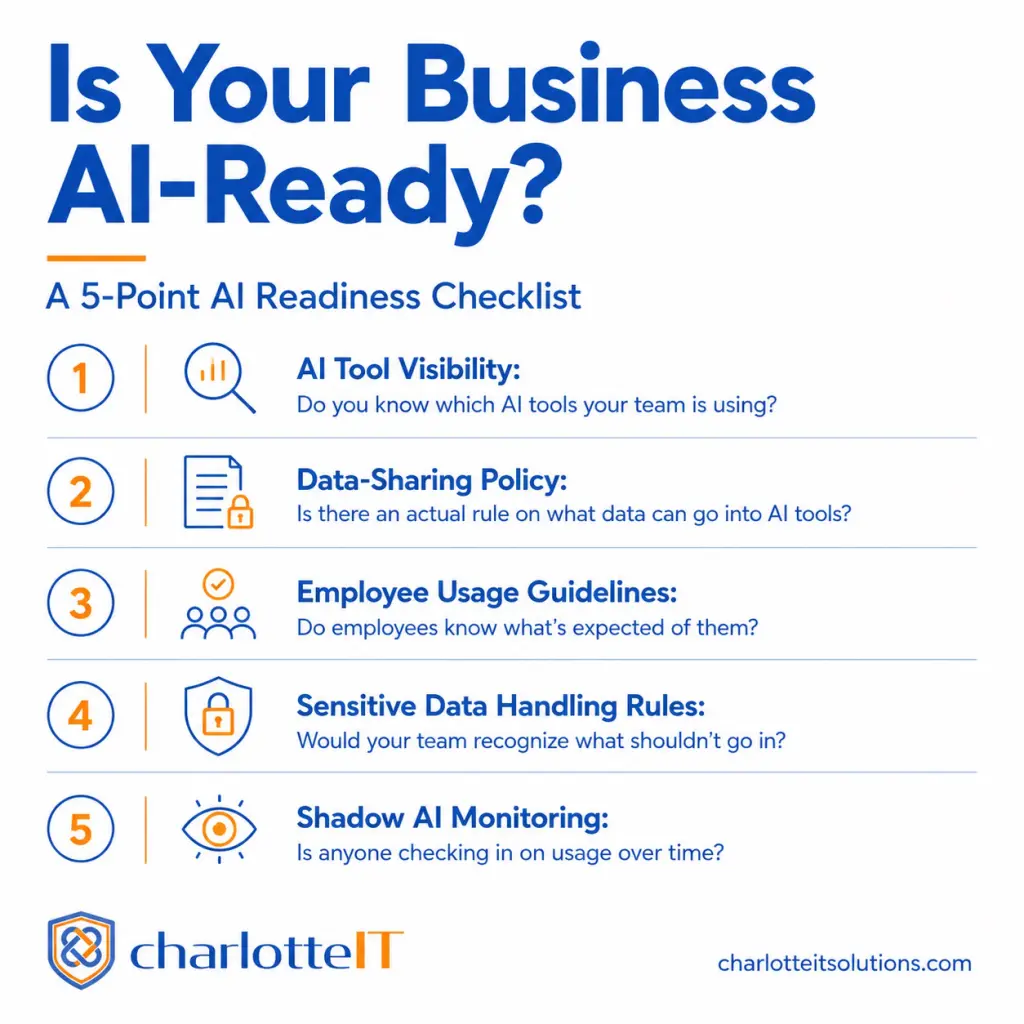
1. AI Tool Visibility
The question: Do you actually know which AI tools your team is using?
Most businesses don’t. Verizon’s 2026 Data Breach Investigations Report found that regular AI use on corporate devices jumped from 15% to 45% in a single year. That’s a fast enough shift that most IT policies haven’t caught up.
You can’t govern what you can’t see. The first step in any AI readiness plan is simply finding out what’s already happening: which tools, how often, and for what kinds of tasks.
2. Data-Sharing Policy
The question: Is there an actual policy on what kind of data can go into an AI tool, or is it just assumed?
KPMG research found that more than half of organizations have no formal policy governing employee use of external AI tools. That’s not a hypothetical for most businesses. That’s the current default.
A data-sharing policy doesn’t need to be complicated. It needs to exist, and it needs to clearly answer one question for employees: what’s off-limits to paste into an AI tool, and what’s fine.
3. Employee Usage Guidelines
The question: Do your employees know what’s expected of them when it comes to AI, or are they making individual judgment calls?
Without clear guidelines, every employee ends up drawing their own line for what feels acceptable. That’s a lot of inconsistent decision-making happening across a business, usually with no bad intent behind it, just nobody’s ever told them otherwise.
Usage guidelines should be simple and specific: which tools are approved, what tasks they’re appropriate for, and what always requires a human double-check before anything goes out the door.
4. Sensitive Data Handling Rules
The question: Would your team know sensitive data if they saw it about to go into an AI tool?
This is the piece that turns a convenience into a real exposure. Client records, financial details, proprietary business information, anything with personally identifiable information. All of it can end up inside a free AI tool’s training data with a single copy-paste. Often, there’s no way to get it back out.
Sensitive data handling rules should spell out, in plain language, the categories of information that should never go into a public AI tool. That holds true no matter how helpful it seems in the moment.
5. Monitoring for Shadow AI
The question: Is anyone actually keeping an eye on this after the policy gets written?
A policy without ongoing monitoring tends to fade in relevance within a few months, which is exactly the kind of gap IT security teams are built to close. This is where “shadow AI” comes in, the term for AI tools employees adopt on their own, outside of anything IT has approved or reviewed. It’s the AI-era version of employees signing up for unapproved apps, except the stakes are higher because these tools process and can retain the data fed into them.
TThis isn’t just best practice. It’s part of how the NIST AI Risk Management Framework defines responsible AI governance. Continuous monitoring, not a one-time policy, is how organizations catch risk as tools and usage evolve.
Ongoing monitoring doesn’t mean policing every employee’s browser. It means checking in periodically on what’s being used. It means revisiting the policy as new tools show up, and catching drift before it becomes a real incident.
Why This Is Easier With an IT Partner
Building an AI readiness checklist is one thing. Keeping it current is another. New AI tools show up constantly, and employees find new use cases on their own. A policy that made sense six months ago can quietly fall out of date without anyone noticing.
This is where having managed IT services in the loop makes a real difference. AI governance stops being a one-time project someone has to remember to revisit. Instead, it becomes part of an ongoing conversation, the same way security monitoring, backups, and business continuity planning already are. A good IT partner helps identify what’s actually in use and builds a policy that fits how your team really works. They also keep an eye on things as new tools and risks emerge.
If AI hasn’t come up yet in a conversation with your IT support provider, that’s worth changing.
Frequently Asked Questions
What is an AI readiness checklist?
An AI readiness checklist is a set of practical steps a business can review. It covers how the business is using AI internally, whether the right policies and guidelines are in place, and where governance gaps exist.
Do small businesses actually need an AI policy?
Yes. Research from KPMG found more than half of organizations have no formal policy governing employee AI use. That’s despite AI tools already being part of daily work for most teams. The gap between usage and governance is the actual risk.
What is shadow AI?
Shadow AI refers to AI tools, apps, or services employees use for work without formal approval, visibility, or oversight from IT or leadership. It’s one of the fastest-growing categories of technology risk.
What data shouldn’t be shared with AI tools?
As a general rule, never enter client records, financial information, or anything containing personally identifiable or proprietary business information into a public or free-tier AI tool. That only changes with a clear data protection agreement in place.
Is banning AI tools the right approach?
Generally, no. Employees adopt AI tools because they’re genuinely useful, and outright bans tend to push usage further underground rather than eliminating it. A governance approach, visibility, policy, guidelines, and monitoring, is more effective than prohibition.
Can an IT partner help with AI governance?
Yes. AI governance works best as an ongoing process rather than a one-time policy document. An IT partner can help identify what tools are actually in use, build practical guidelines, and monitor for new risks as they come up.
When should a business start thinking about AI governance?
Now. AI tool adoption is already happening in most businesses, whether or not there’s a policy in place. Waiting for a formal AI rollout to start governing it means governing something that’s already been in use, unmanaged, for some time.
What’s the first step to becoming AI-ready?
Start with visibility, understanding which AI tools are actually being used across the business today. Every other part of the checklist depends on knowing that first.
The Bottom Line
AI isn’t a future consideration for most businesses anymore. It’s a current one, whether there’s a formal plan behind it or not. The businesses that get ahead of this aren’t the ones banning AI outright. They’re the ones building simple, practical governance around how it’s already being used, ideally with an IT partner helping keep it current.
If you haven’t looked at how AI shows up in your business yet, this is a good place to start.