In today’s digital landscape, implementing robust data privacy best practices is not just recommended, it’s essential for every business, especially small businesses in Charlotte. While large corporations often make headlines for data breaches, it is local small and medium-sized businesses that frequently bear the brunt of cyberattacks due to weaker defense systems. Discover the crucial steps to protect your sensitive information and build consumer trust.
Key Insights
Data Minimization is Critical – Collecting only essential data reduces your exposure to potential breaches and simplifies protection efforts for any small business.
Encryption and Access Controls are Non-Negotiable – Utilize strong encryption for data in all states and enforce strict access limitations to safeguard sensitive information from unauthorized eyes.
Employee Training is a Primary Defense – Educating employees on data privacy and security practices significantly mitigates risks stemming from human error, which is a leading cause of breaches.
Regular Audits Enhance Security – Routinely reviewing and purging unneeded data strengthens your network and closes potential vulnerabilities that old, forgotten data might create.
Compliance Builds Trust – Adhering to relevant data privacy laws and regulations not only avoids penalties but also establishes crucial consumer trust in your business practices.
Understanding Data Privacy and Its Importance
What is data privacy? Data privacy, also known as information privacy, concerns the proper handling of sensitive data. It involves ensuring that individuals’ personal information is collected, stored, processed, and shared according to their consent, organizational policies, and legal requirements. For any organization, particularly small businesses, understanding and respecting data privacy is paramount not just for legal compliance but for maintaining customer relationships. Protecting sensitive data builds confidence with your clients.
Why are data privacy best practices important? Your customers entrust you with their information. Breaches can lead to financial loss, identity theft, and severe reputational damage. Ignoring data privacy can result in significant fines and loss of consumer confidence, which can be devastating for local businesses in the Charlotte area.
Data Security vs. Data Privacy: A Clear Distinction
It’s common to use data security and data privacy interchangeably, but they refer to distinct concepts. Data security focuses on protecting data from unauthorized access, corruption, or theft through technical and procedural safeguards. This includes firewalls, antivirus software, and encryption. Data security measures like these help to keep customer data secure from external threats.
Conversely, data privacy is about how data is collected, used, and shared. It defines who has access to data and under what conditions. While data security provides the tools to protect data, data privacy dictates how that data should be protected and used responsibly. For example, encrypting customer payment information is a security measure, but defining who can view that information and for what purpose falls under data privacy.
Key Steps to Ensure Data Privacy
Minimize Data Collection
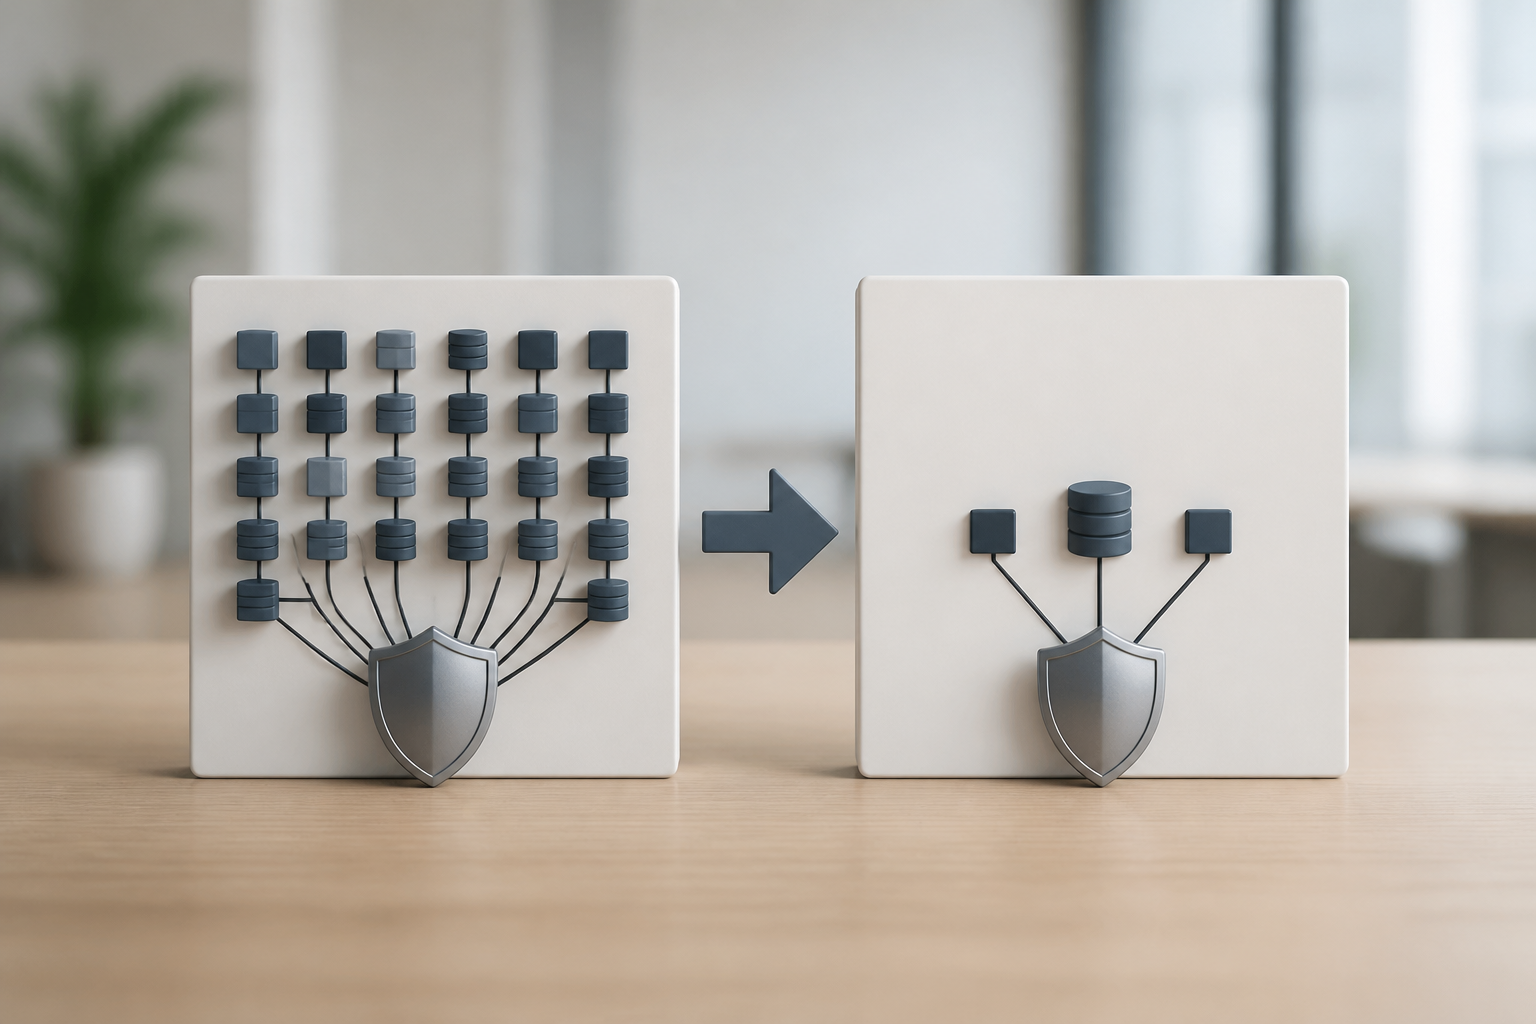
One of the most effective data privacy approaches is minimal data collection. Only collect the information absolutely necessary for your business operations. Over-collecting data not only increases your storage burden but also dramatically expands your attack surface. Think of your data as a plot of land and your network security as a fence. The more land you have, the bigger the fence you need, and the more potential weak points there are for breaches. By collecting less, you reduce your overall risk and the resources needed for protection.
Implement Robust Access Controls and Encryption
Limiting who can access sensitive data is foundational. Utilize strong authentication methods, role-based access, and the principle of least privilege, meaning employees only have access to the data they absolutely need for their job functions. Furthermore, always encrypt sensitive data, both at rest and in transit. Encryption acts as an additional layer of defense; if a cybercriminal bypasses your network defenses, encrypted files will render their efforts largely useless, as they lack the decryption key. For insights into strengthening your digital doors, explore password security tips.
Regular Audits and Data Retention Policies
Do not forget to audit your data regularly. Over time, businesses accumulate data they no longer need. Routinely review your stored information and safely dispose of data that has served its purpose. Implementing clear data retention policies ensures that data is not kept longer than necessary, further reducing your risk profile. Any old devices containing sensitive data that are no longer in use should be securely wiped or removed from your network.
Employee Training and Awareness
Human error remains a top cause of data breaches. Therefore, educating your employees about data security is paramount. Regular training should cover recognizing phishing attempts, avoiding suspicious links, and understanding the importance of strong passwords and secure browsing habits. You can learn more about cybersecurity awareness training for employees. Employees are your first line of defense; empower them to protect your business. Preventing internal IT security threats often begins with informed staff.
Privacy by Design
Integrate privacy considerations into all stages of system and service development. Privacy by Design means making privacy a default setting rather than an afterthought. This proactive approach helps embed privacy protection directly into your operations, from data mapping and inventory to system architecture.
Incident Response Plan
Even with the best precautions, data breaches can occur. Having a clear and tested incident response plan is crucial. This plan should outline steps for containment, investigation, notification (including informing affected customers), and recovery. Transparency with customers about breaches, while difficult, reinforces trust and allows them to take necessary precautions.
Data Privacy Laws and Regulations
How are data privacy laws evolving? The landscape of data privacy is constantly changing, with new regulations emerging globally and domestically. Common data privacy regulations include GDPR (General Data Protection Regulation) in Europe, CCPA (California Consumer Privacy Act) in the US, and HIPAA (Health Insurance Portability and Accountability Act) for healthcare data. These laws grant consumers stronger rights over their personal data, including the right to access, correct, and delete their information. Compliance with these laws is not optional for businesses dealing with such data. HIPAA IT compliance, for example, is critical for medical practices.
Many industries, particularly healthcare and finance, have specific regulatory requirements that mandate stringent data protection. For example, Charlotte IT Solutions helps businesses in the medical sector meet and surpass compliance requirements for sensitive patient records. Adhering to these regulations ensures legal standing and demonstrates a commitment to robust small business data security.
Building Consumer Trust Through Privacy
How can organizations build consumer trust through privacy? Transparency is key. Clearly communicate your data collection practices, how data is used, and the measures you take to protect it. Provide customers with easy ways to manage their data preferences and exercise their rights. A proactive and transparent approach to data privacy demonstrates respect for your customers, fostering loyalty and trust. This also enhances your brand reputation, making your business more appealing to clients who value their privacy.
The Role of AI in Data Privacy
What is the role of AI in data privacy? Artificial intelligence is increasingly employed to enhance data privacy and security. AI tools can analyze vast amounts of data to detect anomalies and potential security threats more rapidly than human analysts. They assist in data classification, identifying sensitive information, and automating de-identification or anonymization processes. While AI offers powerful capabilities for protection, it also introduces new privacy challenges, such as ensuring AI models are unbiased and do not inadvertently expose sensitive patterns.
Protecting Your Business with Charlotte IT Solutions
Ensuring comprehensive data privacy is a complex and ongoing effort. Our team of IT professionals specializes in helping Charlotte businesses implement and maintain the highest data privacy standards. We offer expert guidance on encryption, access controls, compliance, and employee training to keep your data safe and secure.
Request a Free Consultation Today
Frequently Asked Questions
What is data privacy?
Data privacy refers to the responsible handling of personal and sensitive information, ensuring it is collected, stored, processed, and shared in accordance with consent, policies, and legal regulations. It empowers individuals with control over their own data.
Why are data privacy best practices important?
Data privacy best practices are crucial to protect sensitive information from breaches, prevent financial losses and identity theft, maintain legal compliance, and build strong consumer trust. Neglecting them can lead to significant penalties and reputational damage.
How does data privacy relate to data security?
Data privacy defines the rules for how data should be handled responsibly, while data security provides the tools and methods to protect that data from unauthorized access or theft. They are distinct but interdependent; you cannot have true data privacy without effective data security.
What are the key steps to ensure data privacy?
Key steps include minimizing data collection, implementing strong encryption and access controls, conducting regular data audits, establishing clear data retention policies, training employees on security, adopting Privacy by Design principles, and having an incident response plan.
How are data privacy laws evolving?
Data privacy laws are constantly evolving globally, granting individuals greater control over their personal data. New regulations frequently emerge, expanding the scope of protected data and imposing stricter compliance requirements and penalties for non-adherence. Staying informed and adaptable is essential for all businesses.